Detection identifies a suspicious interaction. The next decision is whether to end it or observe it inside a separately isolated environment, without putting production at risk.
An alert arrives from a supervisory interface in a power system. A session is requesting information it does not normally need, or issuing commands outside its expected pattern. The operating team has two immediate questions: what must be protected, and what evidence is needed to respond?
Ending the session may be the right answer. In operational technology, the consequences can include lost control, interrupted service or unsafe physical behavior. Keeping an interaction alive merely to learn more is not a sound default.
There is another option in some architectures: protect the live system while allowing a controlled interaction to continue in a separate engagement environment. That option has value only when the boundary, objective, monitoring and authority to stop are established first.
Detection does not choose the response
A detection can establish that an observed pattern deserves attention. It does not automatically establish the actor’s identity, intent, access or ability to affect equipment. Those are different conclusions, requiring different evidence.
A suspicious command sequence might reflect hostile activity, a misconfigured integration or an authorized task performed incorrectly. Response planning must account for uncertainty while protecting the facility. The team should define in advance which observations justify immediate containment and which can be investigated under controlled conditions.
NIST’s Guide to Operational Technology Security places security controls in the context of OT performance, reliability and safety. It includes incident-response preparation and containment. The operating consequence of a response therefore belongs in the decision alongside the security alert.
Containment and learning have different objectives
Containment seeks to limit harm and regain control. Observation seeks evidence that can improve the next defensive decision. Neither objective excuses exposing production to an unbounded interaction.
For a team considering deception, the useful question is specific: what could an isolated interaction reveal that would change our response? Examples include the sequence of attempted actions, the information sought or the assumptions embedded in the interaction. These are observations about behavior, not proof of identity or a complete account of intent.
Collecting more data without a decision objective adds analysis burden. A narrow question, such as whether an interaction attempts a particular class of supervisory action, is more useful than an open-ended instruction to keep watching.
A separate environment changes the choice
A synthetic environment can represent selected system behavior without giving the interacting session control of the operating facility. Our earlier article, What an Isolated Digital Twin Changes in OT Cyber Defense, explains this architectural distinction.
Credibility and isolation require separate evidence. A model that responds plausibly may support observation, but plausible behavior does not establish that it is separated from production. A separate environment also does not guarantee that an actor will engage, remain engaged or behave as they would against a real facility.
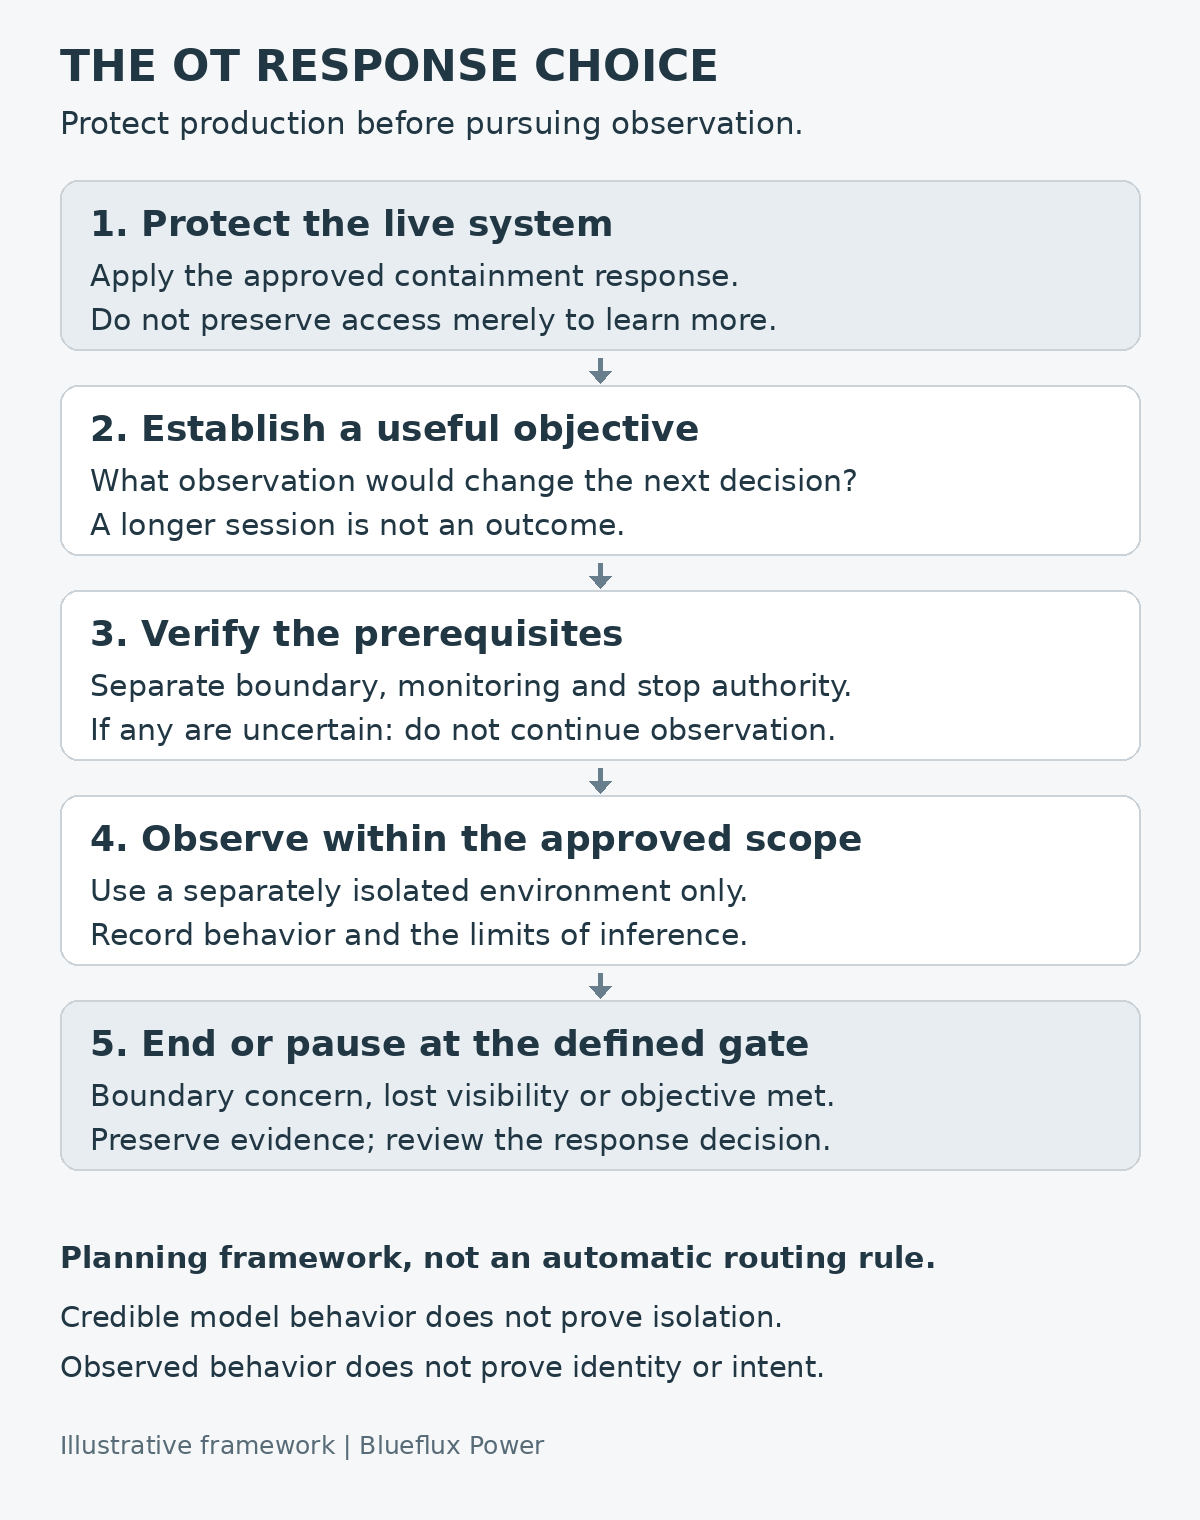
The framework below is a planning aid. It does not describe an automatic redirection mechanism or a Blueflux product implementation.
Define the gate before the interaction
MITRE’s practical guide to adversary engagement describes objectives, rules of engagement and conditions that require an operation to pause or end. Applying that planning discipline to OT leads to four questions:
- Objective: What observation would change a defensive decision?
- Boundary: What evidence establishes separation from production and limits effects beyond the environment?
- Visibility: Who monitors the interaction and can interpret what is collected?
- Stop authority: Who can end it, and what conditions require that action?
These are prerequisites, not assurances of success. The assessment should include unintended communication paths, handling of collected artifacts and changes that could invalidate the boundary. If monitoring is lost or isolation is uncertain, continued observation is not justified by the possibility of learning more.
Choose evidence quality over session length
A longer interaction is not inherently a better outcome. An operation may end because the objective has been met, useful evidence has stopped accumulating or a predefined limit has been reached. The record should explain which conclusion the evidence supports and which conclusions remain uncertain.
Operational owners also need a clear handoff. Security findings should connect to a response decision, configuration review or validated test. Observations from a synthetic model should not be treated as proof of how the live facility would behave.
For infrastructure leaders, the purchasing question is practical: can the team explain the protection boundary, investigation objective, staffing requirement and exit conditions before the demonstration begins? A convincing display is a weak substitute for that operating plan.
Deception can add an investigation option to an OT response architecture. It earns that role through bounded purpose and evidence, while containment remains available whenever production protection requires it.
Decision question: What evidence would make continued isolated observation useful, and what condition would require your team to end it?